Automation. On your terms.
A tool that can change every computer you manage has to answer for each change. Overseer acts on its own only inside limits a named person has set, shows you what it would do before it does it, and records who authorised every action.
Named authorisations
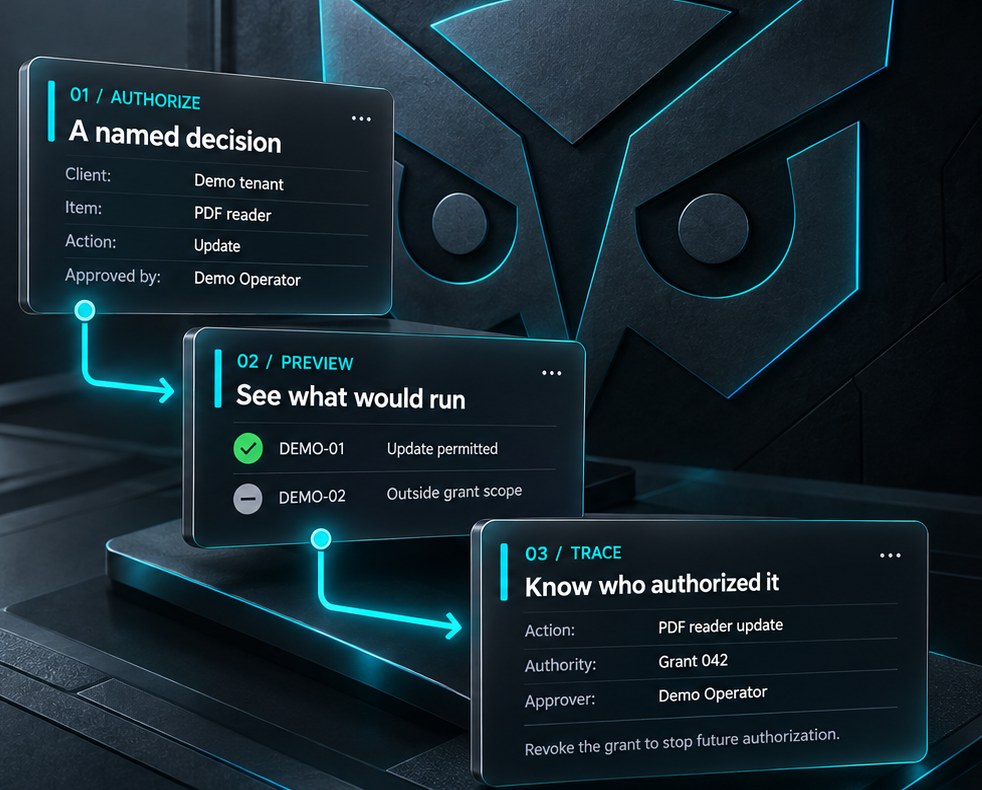
A standing authorisation is a named grant, scoped by client, item and action. Overseer acts on its own only inside it.
Preview before trust
See exactly what would run, and what would be refused, with every action disabled.
Access by role
People see and do only what their role allows. Each client’s computers, deployments and history stay apart.
A full record
The audit log keeps who did what, when and on whose authority. It is kept in full.
Unattended work with no owner is a risk.
- Nobody decided itA script runs across every client because it could, not because a named person approved that kind of work.
- Everyone can do everythingOne shared level of access means the newest person on the team can reach every client’s computers.
- Work lands at the wrong hourAn update restarts a computer in the middle of someone’s working day, and nobody chose that.
- No answer afterwardsA client asks who changed a computer and why. The history is partial, or gone.
You set the limits. Overseer stays inside them.
- Standing authorisationsApprove a kind of work in advance, by client, item and action. Every action records the grant that allowed it.
- Revoke at any timeRevoking a grant stops it authorising anything further. An action that is already running is not cancelled.
- Windows and restart rulesMaintenance windows say when scheduled work may run. Restart rules allow a restart, forbid it, or ask the person using the computer.
- Failed checks are refusedAn installer whose integrity check fails is refused. Overseer does not force it onto the computer.
A decision first. A record after.
Grant
A named person authorises a kind of work for a client, an item and an action.
Preview
Overseer shows exactly what it would run under that grant, with actions disabled.
Record
Each action Overseer sends records the grant that allowed it, in the audit log.
Every change has an answer.
Scheduled work keeps to its maintenance window, unattended work needs a live grant, and every action lands in the audit log with the authority it ran on.
In development. Launch inquiries welcome.
Overseer is still being built and is not available yet. If you would like to hear when it launches, get in touch.